| Edit | Map | Home |  |
New Post | New Gallery |
Support
|

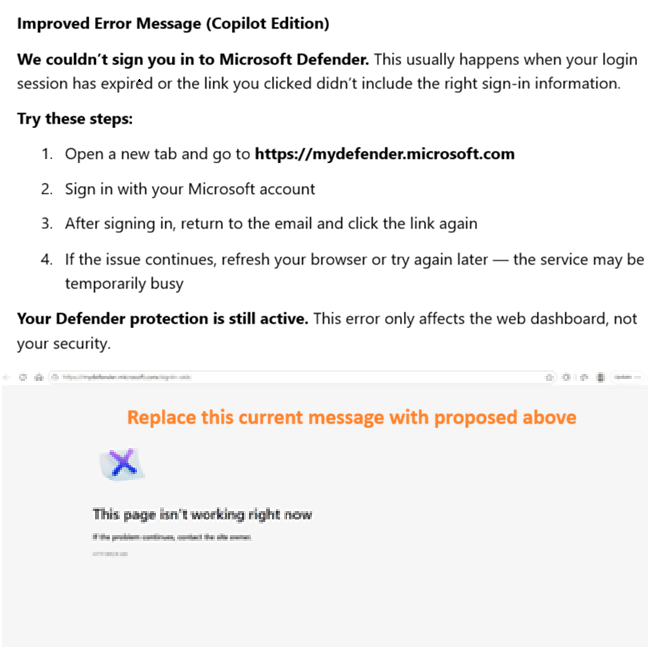 | |
Please rate proposed improved messages sent to users or/and offer your own versions: 1. Message 1 Improved Error Message (Copilot Edition) - We couldn’t sign you in to Microsoft Defender. This usually happens when your login session has expired or the link you clicked didn’t include the right sign‑in information. Try these steps:
Your Defender protection is still active. This error only affects the web dashboard, not your security. ???? Why this version is better It:
2. Message 2 Below is the message Defender should show — calm, clear, human, and designed to prevent panic while still guiding the user to the right action. - ⭐ Improved “What to do right away” message (Cop E Edition) Stay calm — your device is safe. We found some older account information from 2025 in a public breach database. This does not mean your computer was hacked, and it does not mean someone is inside your accounts. What was exposed
What you should do If you used the same real password on any websites back in early 2025, simply update those passwords now. If you didn’t reuse passwords, you’re already safe — no further action is needed. Why this isn’t urgent This breach is from February 2025, and the exposed password is not your actual password. Your device protection is active, and your accounts remain secure. Recommended next step Change the password on any site you know was breached — for example, SeekingAlpha, which recently notified you. Then mark this alert as done. ⭐ Why this message works It:
See the full transcript here: to check how close were you in your reconstruction of events based on the screenshots
|

Author: magludi1 Version: 1 Prototype: => cope scam defender part 1 1 v1 0 Language: English Views: 0
|
Short link: https://www.sponsorschoose.org/a697
Short link to this version: https://www.sponsorschoose.org/n736
Created by magludi1 at 2026-08-18 18:22:53
Last modified by magludi1 at 2026-08-18 18:37:46
|